The California Confidentiality of Medical Information Act (CMIA) is the state’s main medical privacy law. It bars providers, health plans, and contractors from disclosing medical information without written authorization, unless the law allows it.
Enacted in 1981, CMIA predates HIPAA by 15 years and gives patients something HIPAA does not. A patient can sue for $1,000 in nominal damages if records are negligently released, without proving harm. Penalties reach $250,000 per violation when medical information is used for financial gain.
Billing teams feel this directly, since every claim sent to a payer, clearinghouse, or collection agency discloses medical information. This guide explains what CMIA requires, how it applies to billing, its penalties, and how it differs from HIPAA.
What Is the California Confidentiality of Medical Information Act?
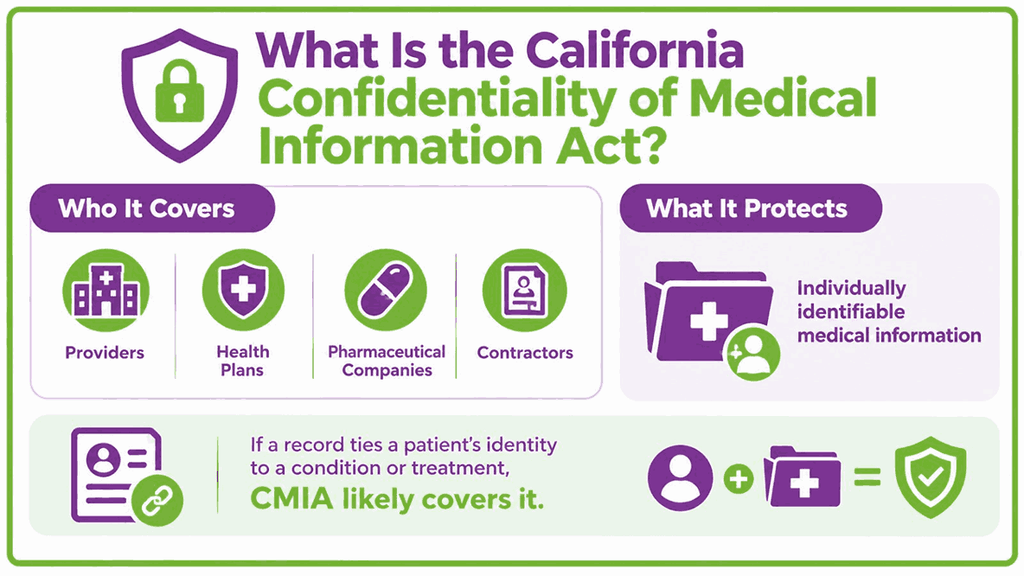
CMIA protects individually identifiable medical information held by providers, health plans, pharmaceutical companies, and their contractors. If a record ties a patient’s identity to a condition or treatment, CMIA likely covers it.
Its reach extends beyond clinics. It also covers businesses that maintain medical information and some digital health apps, so billing vendors and software companies can fall under it.
What Counts as Medical Information Under CMIA?
Medical information is any individually identifiable information, in electronic or physical form, about a patient’s medical history, mental or physical condition, or treatment. Mental health application information now falls within that definition.
Three conditions must be met. The information must identify a person, come from a covered entity, and pertain to a provider’s patient.
Information is identifiable when it contains an element, such as a name or address, that reveals who the person is, alone or with public data.
Who Must Follow CMIA?
CMIA applies to health care providers, health care service plans, pharmaceutical companies, and contractors. Providers include anyone licensed or certified under the Business and Professions Code, such as physicians and clinics. Knox-Keene plans count as health care service plans.
Businesses organized to maintain medical information for patient management also count. So do vendors of software or hardware, including mobile apps, that let consumers manage their medical information.
Anyone who receives medical information from a covered entity for billing or administrative work must follow CMIA’s limits on further disclosure. CMIA’s definition of contractor is narrow and covers medical groups, independent practice associations, pharmaceutical benefits managers, and medical service organizations.
| Covered Party | Examples |
|---|---|
| Providers of health care | Physicians, clinics, and others licensed under the Business and Professions Code |
| Health care service plans | Plans regulated under the Knox-Keene Act |
| Pharmaceutical companies | Companies that hold patient medical information |
| Contractors | Medical groups, independent practice associations, pharmaceutical benefits managers, and medical service organizations |
| Businesses that maintain medical information | Organizations set up to manage patient records |
| Consumer health apps | Software or hardware, including mobile apps, that lets consumers manage medical information |
| Recipients of medical information | Billing companies and clearinghouses that receive information from a covered entity |
How Has CMIA Changed Since 1981?
CMIA began in 1981 as a rule for providers and plans. Amendments have since extended it to businesses that maintain medical information and consumer health apps. Businesses that offer mental health digital services are now covered too.
What Does CMIA Require?
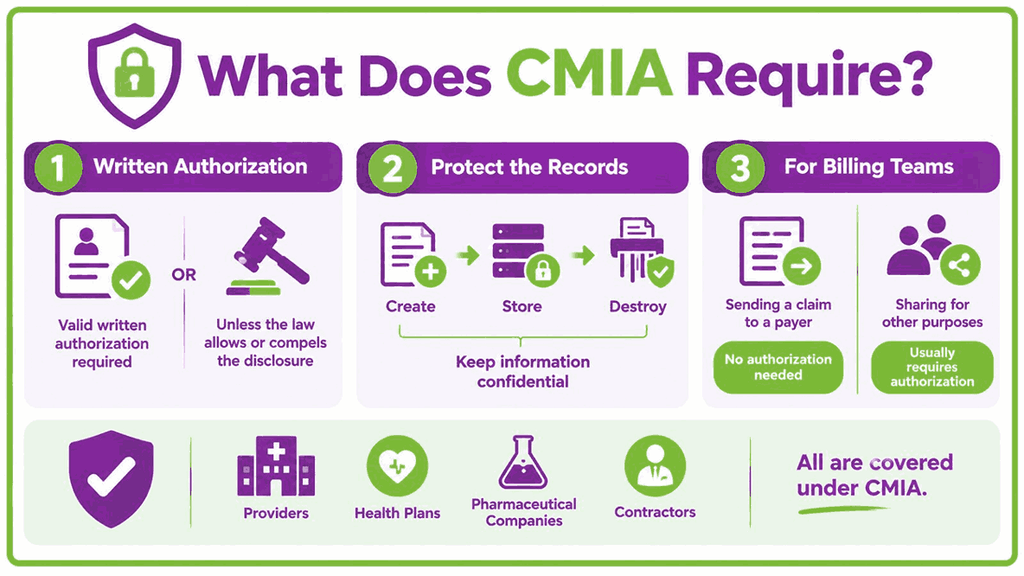
CMIA requires a valid written authorization before a covered entity discloses medical information, unless the law allows or compels the disclosure. It also requires that records be created, stored, and destroyed in ways that protect confidentiality.
For billing teams, the key point is that sending a claim to a payer needs no authorization, while sharing information for other purposes usually does.
When Is Written Authorization Required Under CMIA?
Section 56.10 sets the default rule. A provider, health plan, or contractor cannot disclose a patient’s medical information without first obtaining authorization, except as the law specifies.
Another provision, Section 56.13, adds that a disclosure is lawful only with an authorization that meets Section 56.11, or as other provisions permit or require.
When Can Medical Information Be Shared Without Authorization?
Many exceptions apply. Authorization is generally not required for disclosures tied to diagnosis, treatment, billing, emergencies, licensing and accreditation, utilization review, and quality assurance.
Disclosures to the party responsible for paying for care also fall within the exceptions. Some disclosures are compelled, for example, by a court order, and Section 56.10(b) governs those.
| Situation | Authorization needed? |
|---|---|
| Sending a claim to the patient’s health plan | No, payment disclosures are permitted |
| Sharing records with a treating provider | No, treatment disclosures are permitted |
| Disclosure ordered by a court | No, compelled disclosures follow Section 56.10(b) |
| Release for a reason outside the listed exceptions | Yes |
What Makes an Authorization Valid?
A valid authorization must be handwritten by the signer or typed in at least 14-point type. It must be clearly separate from other language on the page and signed with a signature that serves no other purpose.
The patient or an authorized representative must sign and date it. Further content rules in Section 56.11 mean templates should be reviewed against the statute.
How Must Records Be Stored and Tracked?
Under Section 56.101, every provider, health plan, pharmaceutical company, and contractor must create, maintain, store, and dispose of medical information in ways that preserve confidentiality.
Electronic health and medical record systems must also protect the integrity of information. They must automatically record and preserve any change or deletion, including who made it, when, and what changed.
How Does CMIA Apply to Medical Billing?
CMIA lets providers share medical information for billing, but only as much as the billing work requires. Every claim, statement, and vendor handoff passes patient information to someone else, so each step falls under the law’s disclosure rules.
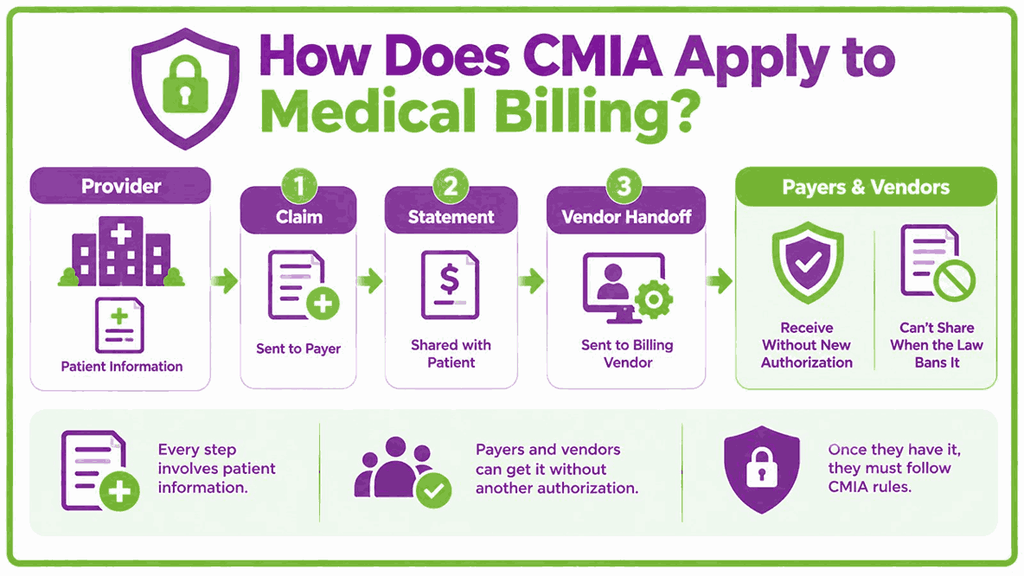
Payers and billing vendors can receive that information without a new authorization. Once they have it, they cannot share it in ways the law bars. Disclosure checks should not slow submission, since payers enforce california timely filing windows.
Can Providers Share Patient Information With Payers Without Authorization?
A provider may disclose medical information to the person or entity responsible for paying for the patient’s care. Disclosure is allowed to the extent needed to determine responsibility and make payment. Claims should include only what the payer needs.
A governmental program exception also covers determining eligibility and obtaining payment, which matters for Medi-Cal claims. Those claims follow separate Medi-Cal billing regulations.
How Does CMIA Apply to Billing Companies and Clearinghouses?
A provider may disclose medical information to a person or entity that provides billing, claims management, medical data processing, or other administrative services. That recipient cannot disclose it further in any way that would violate CMIA.
CMIA’s own definition of contractor is narrow. It covers medical groups, independent practice associations, pharmaceutical benefits managers, and medical service organizations, so billing vendors are bound as recipients. HIPAA business associate agreements apply separately.
Which Billing Activities Need Extra Care?
A provider cannot intentionally share, sell, or use medical information for marketing or any purpose not necessary to provide health care services. The only exceptions are express patient authorization and uses the law allows.
Sending information to collection agencies or other parties outside payment and billing administration should rest on a documented exception or a signed authorization. A practice also cannot make signing an authorization a condition of treatment when it would permit disclosures the law otherwise bars.
| Billing Step | Basis for the Disclosure |
|---|---|
| Claim to the patient’s health plan | Payment exception, limited to what determines responsibility and makes payment |
| Data sent to a billing company or clearinghouse | Billing and administrative services exception, with no further disclosure that violates CMIA |
| Marketing use or sale of patient information | Express patient authorization |
| Referral to a collection agency | Confirm an exception or obtain authorization first |
What Are the Penalties for CMIA Violations?
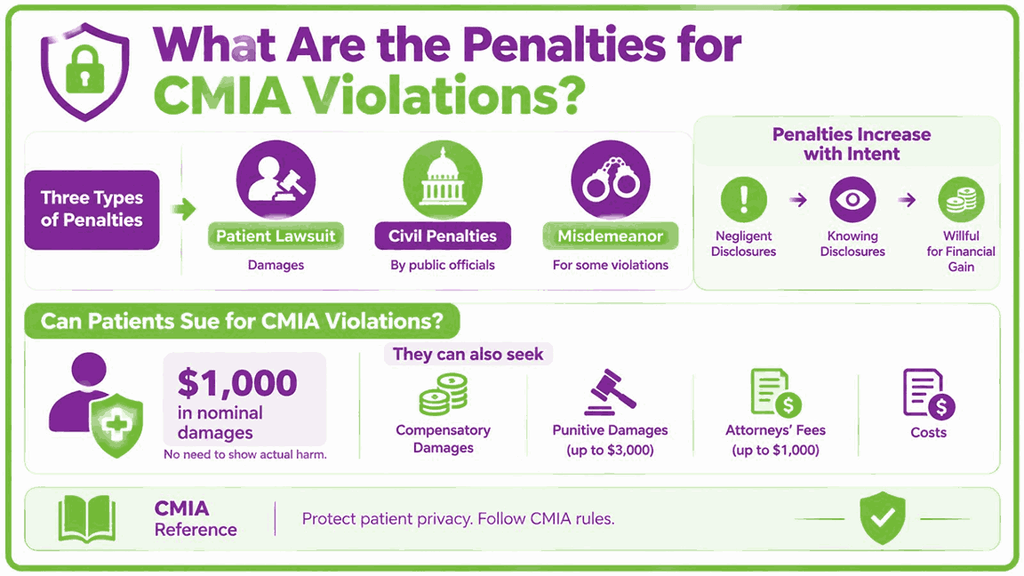
CMIA penalties come in three forms. Patients can sue for damages, public officials can seek civil penalties, and some violations can be prosecuted as misdemeanors.
Penalties increase with intent, from negligent disclosures to knowing, willful disclosures made for financial gain.
Can Patients Sue for CMIA Violations?
A patient can sue anyone who negligently releases confidential records for $1,000 in nominal damages. The patient does not have to show actual harm. Actual damages can be added when they exist.
A patient with economic loss or personal injury can also seek compensatory damages, punitive damages up to $3,000, attorneys’ fees up to $1,000, and costs.
Covered entities and business associates can use nominal damages as a defense. They must show, among other things, that the release went only to another covered entity or business associate. They must also show that safeguards such as security policies and encryption were in place.
Even when the defense succeeds, the patient still recovers actual damages and attorney’s fees.
What Civil Penalties and Fines Apply?
Penalties depend on intent and on who committed the violation. The table lists the maximum amount for each category.
| Conduct | Who | Maximum penalty |
|---|---|---|
| Negligent disclosure | Any person or entity | $2,500 per violation |
| Knowing and willful disclosure | Anyone other than a licensed health care professional | $25,000 per violation |
| Knowing and willful disclosure | Licensed health care professional | $2,500 first, $10,000 second, $25,000 third and subsequent |
| Knowing or willful use for financial gain | Anyone other than a licensed health care professional | $250,000 per violation plus disgorgement |
| Knowing and willful use for financial gain | Licensed health care professional | $5,000 first, $25,000 second, $250,000 third and subsequent, plus disgorgement |
| Knowing and willful disclosure without authorization | Anyone not permitted to receive the information | $250,000 per violation |
Who Enforces CMIA, and Can Violations Be Crimes?
The Attorney General, district attorneys, county counsel, city attorneys, and city prosecutors can bring civil actions for penalties. A violation that causes a patient economic loss or personal injury can also be prosecuted as a misdemeanor.
A court weighs several factors when setting an amount. These include good-faith efforts to comply, the seriousness of the misconduct, harm to the patient, the number of violations, and the defendant’s assets.
The terms “knowing” and “willful” carry their Penal Code meanings, so intent matters. Disclosures made under CMIA’s own exceptions are not subject to its penalties.
How Do CMIA and HIPAA Differ?
HIPAA sets the federal floor for protecting health information, and CMIA builds on it for California. Both apply to most California providers, and state rules that go beyond HIPAA remain in force.
Here’s how they both compare at a glance.
| Area | HIPAA | CMIA and California law |
|---|---|---|
| Who is covered | Covered entities and business associates | Licensed providers, health plans, contractors, and certain businesses that maintain medical information |
| Private right of action | None | Patients can sue, with $1,000 nominal damages after a negligent release |
| Civil penalties | Tiered fines of $145 to $73,011 per violation, with a $2,190,294 annual cap | Up to $2,500 negligent, $25,000 knowing and willful, and $250,000 for financial gain, with tiers for licensed professionals |
| Patient record access | 30 days, with one extension | 5 working days to inspect and 15 days for copies under Health and Safety Code §123110 |
| Breach reporting for licensed clinics and facilities | 60 days to notify individuals | 15 business days to report to the state and notify patients under Health and Safety Code §1280.15 |
How Can Practices Stay CMIA Compliant?
Staying CMIA compliant depends on knowing where patient information goes, why it goes there, and who can share it. Written procedures, clean authorization forms, and system logs cover most risks.
These steps also help in court, since safeguards such as security policies and encryption support a defense against nominal damages.
The checklist below will help you stay compliant if you follow it properly.
| Area | What to do | Basis |
|---|---|---|
| Disclosure map | List every recipient of patient data and the exception or authorization behind each | Civil Code §56.10 |
| Authorization forms | Use 14-point type, a separate signature, and signed and dated forms, and never make signing a condition of treatment | Civil Code §§56.11 and 56.37 |
| Vendor handoffs | Confirm vendors cannot disclose information further and sign HIPAA business associate agreements | Civil Code §56.10(c) and HIPAA |
| Records systems | Keep audit logs of changes and deletions and protect record integrity | Civil Code §56.101 |
| Marketing and other uses | Get express patient authorization before any use not needed for care | Civil Code §56.10(d) |
| Staff training | Train staff on the exceptions and the limits on further disclosure | Good practice |
| Incident response | Know the 15-business-day reporting rule if the practice is a licensed clinic | Health and Safety Code §1280.15 |
CMIA covers privacy, but billing teams answer to several California rules in the same claim cycle. Practices that follow every one of the California billing laws that apply to them protect both revenue and patient data.
How Do Safeguards Reduce Legal Exposure?
Section 56.36 lets covered entities and business associates defeat nominal damages in some cases. The defense requires safeguards such as security policies, a designated security official, and encryption, plus corrective action after a release.
It also depends on the release going solely to another covered entity or business associate, so it does not cover every incident. Practices can run these steps in-house or with help from a California medical billing provider.
FAQs
Can a Patient Cancel or Change a CMIA Authorization?
Yes. Anyone who can sign the authorization can cancel or modify it. The change takes effect only after the provider receives written notice, so disclosures made before then remain under the original authorization.
Who Can Sign a CMIA Authorization for a Minor Patient?
A minor patient can sign an authorization only for information tied to services the minor could lawfully have consented to alone. Other cases call for a legal representative’s signature, so staff should confirm the signer’s authority before releasing a minor’s records.
Does CMIA Protect a Patient’s Records After Death?
Yes. CMIA defines a patient as a natural person, whether living or deceased, who received health care services from a provider. A legal representative, spouse, beneficiary, or personal representative can sign an authorization for a deceased patient.
What Should a Practice Do After an Unauthorized Disclosure?
Contain the release, document what happened, and check the notice duties. HIPAA requires notice to affected individuals within 60 days, and licensed clinics and facilities must report within 15 business days. Breaches affecting more than 500 California residents must also be reported to the Attorney General. Prompt corrective action supports the defense against nominal damages.
Who Counts as an Authorized Recipient Under CMIA?
An authorized recipient is anyone allowed to receive medical information under Section 56.10 (provider and plan disclosures) or Section 56.20 (employers). Payers, including plans paying out-of-network claims under AB 72, are examples under Section 56.10. Billing vendors that receive information under the payment and billing exceptions are, too.